Turn suspicious infrastructure reconnaissance into clear security signals.
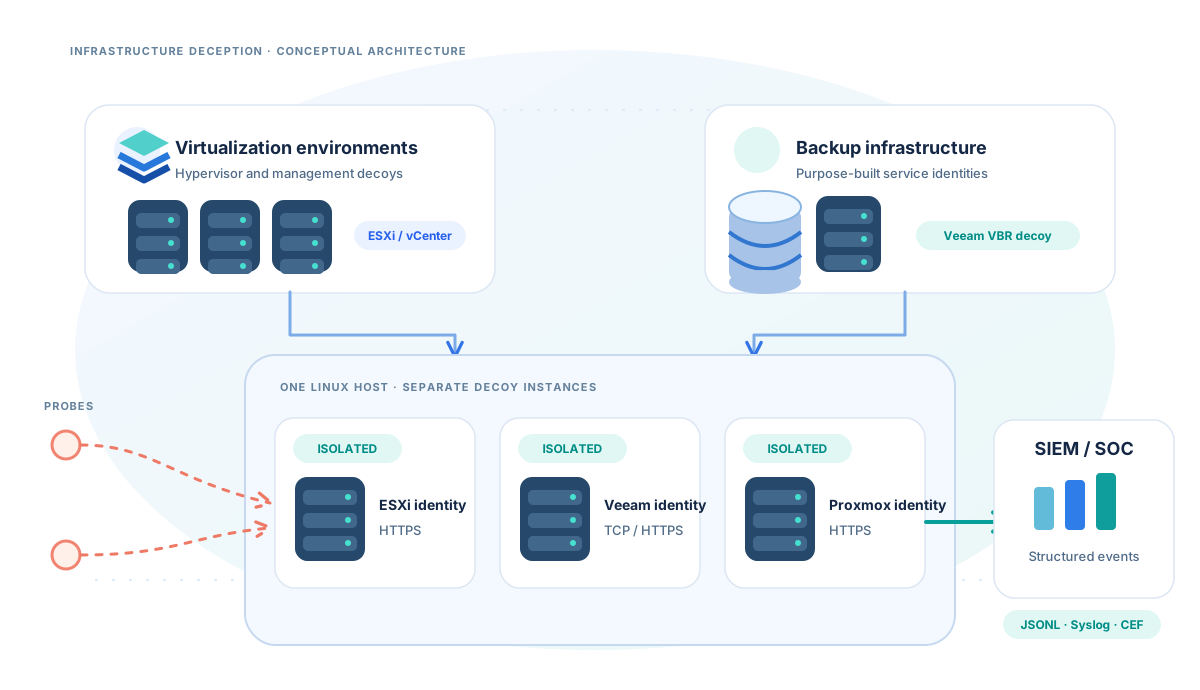
Deploy 23 lab-qualified, product-specific decoys across virtualization, backup, identity, and hardware controllers on a single Linux host. Any unexpected connection becomes a high-fidelity event for immediate SOC investigation.
 VMware vCenter 8 Decoy Interaction
Action Required
 Veeam Backup & Replication Probe
Logged
Detection before damage takes place
Lateral discovery routinely probes management ports and storage endpoints. DecoyStack gives defenders early, high-confidence notification by placing high-value decoys in the attacker path.
Surface unauthorized probing
Legitimate administrative workflows have no business connecting to unmapped decoys. Every touch is an explicit anomaly worth investigating.
Protect critical surfaces
Simulate virtualization management nodes, backup targets, and hardware BMCs that adversaries search for during ransomware staging.
Preserve existing pipelines
Export structured events with rich source context directly into Splunk, Elastic, Sentinel, or QRadar through native JSONL, Syslog, or CEF.
High-context signal against telemetry fatigue
Network sensors produce millions of flow records. DecoyStack anchors incident response with an indisputable starting point.
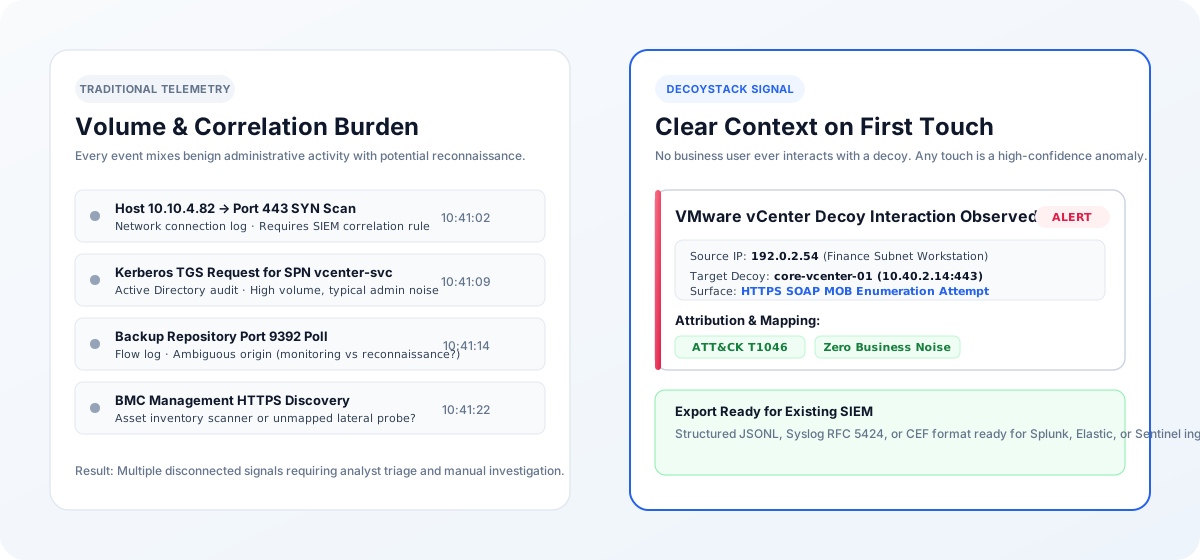
Traditional Sensor Telemetry
Massive log volume requiring extensive correlation queries.
- • Port scan noise blended with routine internal administrative tasks
- • Ambiguous intention requiring multi-hop forensic correlation
- • High alert fatigue leading to delayed containment windows
DecoyStack High-Fidelity Signal
Clear ContextInstant clarity with zero legitimate operational traffic.
- ✓ Decoy touched: Immediate trigger without waiting for baseline drift
- ✓ Full protocol attribution: Identity, requested URI, and TLS fingerprints
- ✓ SIEM-ready: Direct export into SOC workflows without custom rule tuning
Decoys for high-value targets
Deploy 23 lab-qualified decoy profiles matching the enterprise technologies attackers seek during post-exploitation.
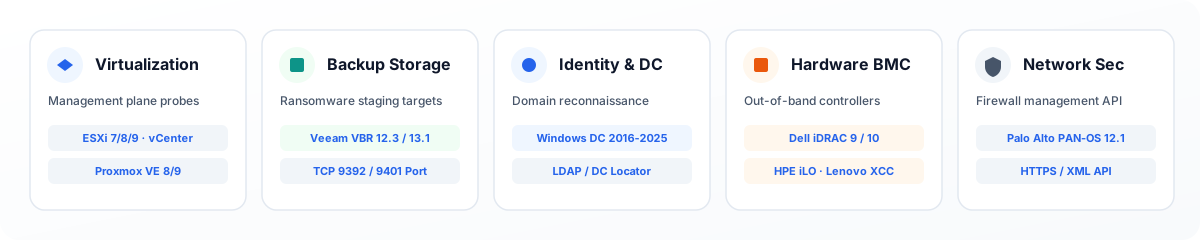
Virtualization
Hypervisor control surfaces and management planes subject to lateral enumeration.
Backup Storage
Targeted repositories that threat actors identify and tamper with prior to encryption.
Identity & Directory
Observe domain discovery and locator calls without placing real domain assets at risk.
Hardware BMC / OOB
Extend detection beyond the OS into physical out-of-band management controllers.
Network Security
Identify unauthorized reconnaissance aimed at perimeter and firewall management APIs.
23 Qualified Profiles
Every profile is qualified through isolated multi-instance testing before inclusion.
Deploy in minutes without virtual machine overhead
Run multiple synthetic identities on a single Linux host without creating and managing dozens of distinct operating systems.
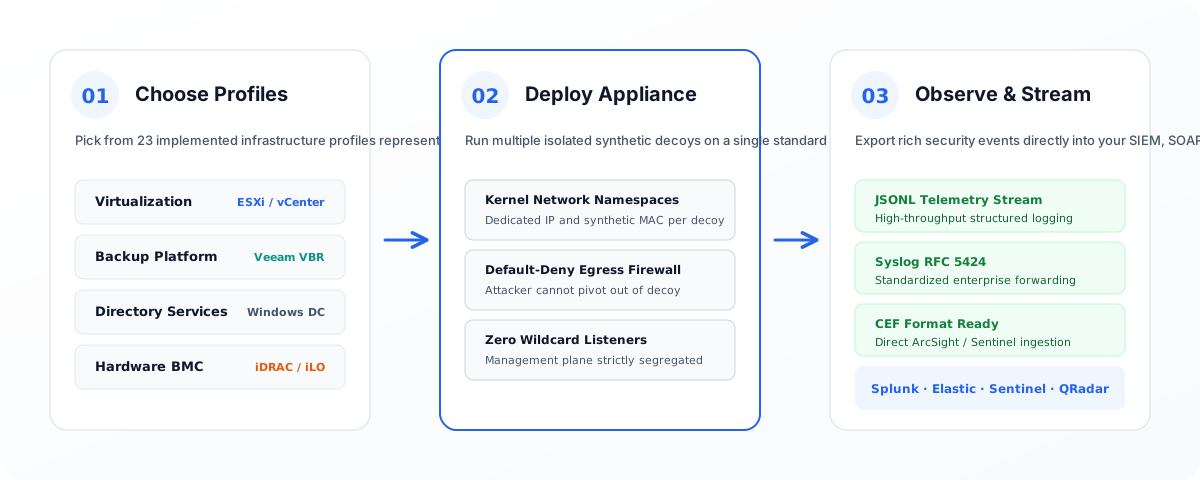
Select profiles
Choose from 23 implemented profiles matching the specific assets and versions running in your production environment.
Deploy appliance
Launch isolated decoy identities on a standard Linux host, each assigned its own dedicated IP address, synthetic MAC, and firewall rules.
Forward to SIEM
Stream structured alerts in JSONL, Syslog RFC 5424, or CEF directly into your existing detection and response infrastructure.
Containment engineered at the kernel level
Decoys intentionally attract malicious attention. DecoyStack isolates each identity to guarantee that probing activity never pivots into the production network.
Default-deny egress
Outbound packets are dropped at the kernel firewall boundary, ensuring the decoy cannot be repurposed as a staging pivot.
Explicit IP binding
Listeners bind exclusively to designated synthetic IP addresses. No wildcard listeners (0.0.0.0) are ever opened on host interfaces.
Unprivileged execution
Each profile daemon runs with unprivileged user accounts within segregated network namespaces, preserving multi-tenant host safety.
Collaborate on early enterprise evaluation
We are working with SOC teams, security architects, MSSPs, and infrastructure engineers to validate decoy placement, detection topologies, and SIEM integrations.
- • Test decoy effectiveness against your adversary emulation scenarios
- • Verify telemetry streaming against your existing ingestion pipeline
- • Evaluate controlled pilot access as release packaging progresses
Technical Preview Notice: Discussions focus on architecture and early validation. No commercial purchase commitment is required.
Apply for Design Access
Tell us about your infrastructure. We will follow up with technical details.